Wednesday, April 20, 2016

Policy Request and Response

A customer of mine has an issue with Policy Evaluation, so I was asked to help him debug.


We know OpenAM Web Policy Agent is PEP (Policy Enforcement Point), while OpenAM Server is PDP (Policy Decision Point). So, an web agent will send a Policy Request to OpenAM server and OpenAM server will send back a Policy Response, all in XML format.

The logs are captured in Policy debug log.


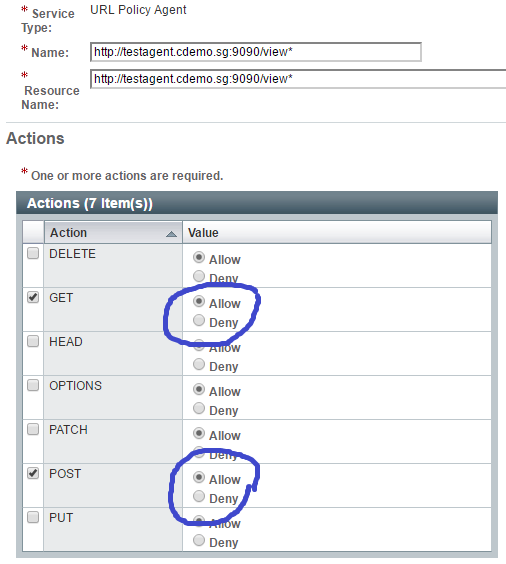
If the policy evaluation returns success, then "allow" will be returned as part of ActionDecision.


This maps well with what is configured in OpenAM Administration Console.


However, do take note that when policy evaluation returns failure, then "deny" is not returned as part of ActionDecision.


Customer thought something was wrong with OpenAM policy evaluation engine because he was expecting DENY to be returned from OpenAM server. 


. 


Wednesday, March 23, 2016

Why IAM Projects Fail?

I was presenting to a potential Identity Management & Governance customer the other day. I talked about Why IAM Projects Fail and the Pain Points from our field experience.

Gartner has this nice diagram to explain Why IAM Projects Fail. A summary can be found here. 


See the proportion of People vs Products? In the market, there is really not much difference between the various IDM/IDG products. I can safely say their features are almost 85-90% similar. It's the implementors & customers' key stakeholders ("People") that makes the difference between a successful and failure IAM project.

A good People combination will spend more time in defining Principles, Practices, Policies and Processes. 


The Pain Points are from our field experience.


Again (coincidentally?), the biggest pain is People.


  • No ownership/main-driver (no full-time PM) 
  • Not trained 
  • Not really know what they really need (Keep changing requirement) 
  • Not enough support from application teams 
  • No well thought-of test plans & not following test plans


Sounds familiar? Well, the fact is we still encounter them in almost all IDM/IDG projects.


.


Wednesday, March 9, 2016

OpenAM - http://null:8080/auth/XUI/#login/

At times, like today, I do encounter http://null:8080/auth/XUI/#login/ error when trying to log in to OpenAM.


A quick workaround is to close the browser and open a new browser or go into Incognito mode.

PS: On the browser that I encountered the above issue, I did have another OpenAM session running. But it was pointing to a totally different domain. No time to think straight yet. :) Just a quick note here since I have captured the logs for further investigation.


Updated on 10th March 2016

Peter was referring to Configuration > Authentication > Core.


I tested in my environment. It worked! Thank you! Thank you!


.

Wednesday, March 2, 2016

OpenAM Fresh Install Issue - HTTP Status 500 - AMSetupFilter.doFilter

Out of laziness, I reused an existing Tomcat instance that had OpenAM 12 installed and configured.

It's fast! 

Stop Tomcat; Remove OpenAM 12 war file and the exploded OpenAM 12 directory; Deploy OpenAM 11 was file; Start Tomcat. 

Bomb! As soon as Tomcat started, I encountered HTTP Status 500 error.


Took me a while to realize that I have not yet cleaned up the hidden OpenAM configuration.

[ec2@am0 ~]$ cd .openamcfg/
[ec2@am0 .openamcfg]$ ls -altr
total 16
-rw-rw-r--.  1 ec2:ec2   25 Mar  1 18:55 AMConfig_data_opt_am1200_webapps_auth_

This file pointed to a configuration directory where OpenAM 12 was previously installed. Now that OpenAM 11 was installed, the above AMSetupFilter.doFilter error appeared.

Stop Tomcat.

[ec2@am0 .openamcfg]$ rm -fr AMConfig_data_opt_am1200_webapps_auth_

Start Tomcat again.


.

Monday, February 29, 2016

OpenDJ with Data at Rest Encryption Solutions Part II

I blogged about OpenDJ with Data at Rest Encryption Solutions few weeks back. The POC was carried out with OpenDJ 2.6.


OpenDJ 3.0 has recently been released and the test equipment (SafeNet Data at Rest Encryption appliance) is still in our office, why not let's run a test again OpenDJ 3.0? :)

In OpenDJ 3.0, there are 2 local DB backends to choose from: JE (Oracle Berkeley DB Java Edition - 2.5 version) and PDB.


The throughtput for search operation is faster in OpenDJ 3.0 as compared to version 2.6. The response times are also slightly faster.


Encrypted partition: 11229 (JE) & 10488 (PDB) vs 10210 (JE)   ~10% diff
Non-encrypted partition: 11305 (JE) & 11235 (PDB) vs 10410 (JE)  ~ 8.5% diff


For write operations, the difference in throughput is not big. In fact, PDB performs worse. (Hmmm... Maybe need to ask my colleague to re-run the test again) ..

Encrypted partition: 2926 (JE) & 2758 (PDB) vs 2750 (JE)   ~6.5% diff
Non-encrypted partition: 3282 (JE) & 2824 (PDB) vs 3199 (JE)  ~ 2.5% diff


The difference in response time is also not big. Again, I might want to re-run the test for PDB again. Or maybe some tuning is required. Not sure, it's something new to me. :)

Encrypted partition: 8.2 (JE) & 8.70 (PDB) vs 8.72 (JE)
Non-encrypted partition: 7.3 (JE) & 8.4 (PDB) vs 7.5 (JE)


.


Monday, February 22, 2016

OpenAM Policy Configuration - High-Availability and Load-Balancing

I realized I blogged this topic before last year - OpenAM Policy Configuration - HA Issue.


One of my customers encountered policy evaluation failure last week due to a fault with one of their OpenDJ servers.

The Policy Configuration (Access Control ++ / (Top Level Realm) ++ Services ++ Policy Configuration) is seldom in use, unless a LDAP Filter condition is configured in Policies (Access Control ++ / (Top Level Realm) ++ Policies)


I'm trying my luck again today to find out a good HA solution for Policy Configuration.


1) The following instructs all OpenAM nodes to communicate with a single OpenDJ server. This is not ideal.


2) The following will not work.

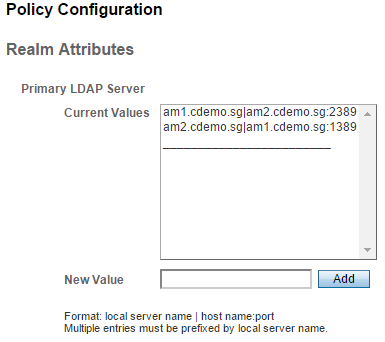
OpenAM debug log will complain with failed to get LDAP server name. If you enter more than one server name in the policy config service's Primary LDAP Server field, please make sure the ldap server name is preceded with the local server name".


3) For multi OpenAM servers, it is better to distribute the load equally to different OpenDJ servers in the backend. However, of course, this doesn't solve the original high-availability/failover issue.


I'm thinking of having 2 entries of the same local server name, each append with a different OpenDJ server. No luck!


Tested. OpenAM only takes the last entry if multiple identical local server name appear. In the above case, only "am2.cdemo.sg:3389" is mapped to "am2.cdemo.sg" (local server name).


The underlying code is such that a local server name can only return a LDAP SERVER entry.

com.sun.identity.policy.PolicyConfig


com.sun.identity.shared.datastruct.CollectionHelper 


Why isn't there a Secondary LDAP Server configuration?


For now, no choice, I think we need a LB in front of the OpenDJ servers.

.

Wednesday, February 10, 2016

OpenDJ with Data at Rest Encryption Solutions

We just completed a POC for a customer few weeks ago. This is a long time customer using Sun Directory Server and subsequently ported over to ForgeRock OpenDJ.


Recently, due to the strict PDPA requirement from the PDPC (Personal Data Protection Commission Singapore), we are to ensure the user profiles stored in OpenDJ are kept totally safe.

So, few weeks ago, we worked with Gemalto engineers to deploy OpenDJ local DB backend on a partition that is protected by SafeNet Data at Rest Encryption.


Worked like a charm!

I asked my colleage to run a little load-test (6 Connections / 4 Threads) using OpenDJ SDK Toolkit for comparison.

The response time for search operation looks pretty similiar. 


 Now, when it comes to write operations, then there is quite a bit difference in the response time.


Need to be careful in deployment sizing when customer decides on this solution.


.

Saturday, February 6, 2016

OpenAM Security Advisory #201601

ForgeRock has just released a security advisory #201601 last night and it is quite a long list - a total of 15 vulnerabilites found in OpenAM 12.0.2, 12.0.1, 11.0.3 and 10.0.2.

I have customers using 12.0.2, 11.0.3 and 10.0.2. Not really good news to me. :(


Details can be found here. Start patching!

Tuesday, February 2, 2016

OpenDJ Naming Conflicts nsuniqueid=xxx

Just realized I took a long break from blogging. So, I took a long holiday in December to make a family trip to Taiwan. Nice place to be in! In fact, I visit Taiwan frequently. This time round, we went to the eastern side of Taiwan - Taitung area. 


So, we have a long time customer who is using OpenDJ as a centralized user store. Few weeks back, he emailed to notify me that he found some "weird" user entries with DN as such:


dn: nsuniqueid=85c95685-21eb11df-80d5c084-e9b4da2d+uid=stageon238,ou=members,o=XXX.sg

A similar entry was found in the same OpenDJ:

dn: uid=stageon238,ou=members,o=XXX.sg


This is a naming conflict that only happens for replayed operations in a MMR setup.

I am not able to find any documentation from OpenDJ. Here are 2 links that talk about this naming conflict:

  1. Resolving Naming Conflicts
  2. Solving Naming Conflicts


In short, remove the entry which is older.


.


Tuesday, November 24, 2015

OpenAM 12 - New Forget Password Self-Service

Most of my customers build their own User Self-Service module. That includes Change Password and Forget Password. And most of the times, they interact with the backend data source (e.g OpenDJ or Active Directory) directly.


I seldom have to worry about enabling the Forget Password feature in OpenAM. Well, good time is up for me. :) I have a customer that wants to utilize the Forget Password in OpenAM 12. 

Well, so based on my past exploration with OpenAM Password Reset feature, our discussion revolved around Challenge Questions & Answers and how the flow will be. Note that this customer only wanted the new XUI. No way to use legacy UI as discovery and customization times have been invested into rebranding the XUI.

Today, I had a shock when I started to read more about the Forget Password feature in OpenAM 12. The more I read, the more confused I become. The documentation keeps talking about Resetting Forgotten Passwords (legacy). 

OpenAM can provide self-service password reset for forgotten passwords when end user pages are served by the classic UI. To enable self-service password reset, you must configure the password reset service itself, which consists mainly of setting up secret questions, and configuring an SMTP mail server to send reset passwords to the users of the service.

But Mr Customer wants nothing, but the new XUI.

Now, during XUI rebranding, I did come across the following scripts in one of the template files.


There is definitely something to configure via the OpenAM Administration console to make the Forget Password hyperlink appears in XUI.

So I searched around and reached Configuration > Global > User Self Service. There you are! The Forgot Password for Users is disabled by default.


So I went ahead to enable the feature. Another great feature out there is the Forgot Password Token LifeTime (seconds). This expires the hyperlink which is sent to users. (Will talk about this in a while ...)


Nice, the Forgot password hyperlink finally appears!


The next screen is what you'll see when the Forgot password hyperlink is clicked.


When a correct username (default is to match with UID) is entered, an email will be sent.


The user will receive an email like the following:


This is where the Forgot Password Token LifeTime (seconds) kicks in. I suppose the hyperlink in the email will expires in the configured time. (I'll need to fully test this function. Still at high-level investigation now)

Once the hyperlink is clicked, the user will be redirected to the Change forgotten password page.


Pretty cool right? Initially I thought Mr Customer would reject it because the long-discussed Challenge Questions & Answers feature is no longer available in the new XUI. But, to my surprise, he prefers this new feature, especially the Forgot Password Token LifeTime.

And what surprised me more?

This new feature is not mentioned at all in OpenAM documentation, not in stable release. And I just searched the draft documentation for OpenAM 13, it's not mentioned as well. Maybe it's hidden somewhere, but it's really not obvious to customers and integrators like us.


The documentation is not catching up with development? Super strange! 


.

Monday, November 23, 2015

SLF4J: Class path contains multiple SLF4J bindings

Prior to OpenAM 12, we used to have our own logging framework using SLF4J and LogBack, instead of default logging framework that comes default with OpenAM. 


In OpenAM 12, multiple SLF4J bindings errors are thrown if both logging framework co-exist.

SLF4J: Class path contains multiple SLF4J bindings.
SLF4J: Found binding in [jar:file:/data/opt/apache-tomcat-8.0.26/webapps/auth/WEB-INF/lib/openam-slf4j-12.0.2.jar!/org/slf4j/impl/StaticLoggerBinder.class]
SLF4J: Found binding in [jar:file:/data/opt/apache-tomcat-8.0.26/webapps/auth/WEB-INF/lib/logback-classic-1.1.3.jar!/org/slf4j/impl/StaticLoggerBinder.class]
SLF4J: See http://www.slf4j.org/codes.html#multiple_bindings for an explanation.
SLF4J: Actual binding is of type [org.forgerock.openam.slf4j.AMLoggerFactory]


Need to handle carefully.

.

Friday, November 20, 2015

OpenAM - Mobile Access

The common topic from customers these days is how to integrate their mobile applications with OpenAM.

I will usually use the material from Shoot Me a Token: OpenAM as an OAuth2 Provider. Victor wrote this quite some time ago when I attended the 1st Open Identity Summit in the US. But it's still relevant.


So, there are a few ways to integrate mobile applications with OpenAM - OAuth2, OpenID Connect or REST. All methods are language independent, which is good.


The most common integration will be OAuth2. With OAuth2 in mind, one has to differentiate that there are in fact 2 types of tokens - Access Token & Refresh Token. The lifetime of a refresh token is long. So, a refresh token is used to exchange for a new access token (which is short-lived). This is important concept. Otherwise, users will need to keep logging in.


A real life example would be your Facebook application on your mobile phone. Are you prompted to log in every day? I don't even recall when did I last logged in. Technically, it's the "refresh token exchanging for an access token" in play.


In order for OpenAM to behave like Facebook (ok, this is very layman), the OAuth2 Provider feature in OpenAM has to be enabled. Once enabled, OpenAM can now provide the same functionalities as Facebook. It is now able to issue access and refresh token to mobile applications. It is now OAuth2-aware.


Some customers will then want to know more about what's going on behind the scene. Well, Victor's slides have it all. I just need to highlight a bit to make it complete.


The very 1st time a user access a mobile application (OAUTH2 Demo), he will be prompted with a consent page.


OpenAM will display the same to user. Depending on which OpenAM version you are using, you might get this:


Yes, so UI customization is required. :)  Or if you might get this:


I have not tested the latest UI yet. (Currently on a OpenAM 12 project, OAuth2 is in next phase)


So, after user has given his consent (highlighted in RED), an attribute in the user's LDAP entry is updated to "remember" user has in fact given his consent. This will prevent the Consent Page to be displayed again.

Once that's done, the mobile application will request for an Access Token and this will be stored in the Key Chain on the handphone (highlighted in BLUE). At the same time, the Refresh Token is stored.


The next time the user fires up the mobile application, it will retrieve the Access Token. If it has not expired, it will be used to request token information from OpenAM.


If the Access Token is expired, then the Refresh Token will be used to exchange for a new Access Token. The new Access Token will be stored in the Key Chain.


The extreme case will be the Refresh Token has also expired. Then users will be forced to re-login again.


That explains why some sites have their Refresh Token set to be months or even year. Just long enough for you to change handphone. :)


Futher readings:

[Concept] Working with Mobile Devices & Applications

[Sample] OpenAM OAuth 2.0 iOS Sample App

* I have not tested the sample codes yet. No comment there.


.